AI Governance Consulting & Implementation Services
Build a secure, governed and compliant foundation for enterprise AI with AI risk assessments, data governance, access controls, responsible AI policies, monitoring and Microsoft security and compliance technologies.
Why Enterprise AI Needs Governance
Uncontrolled AI adoption introduces security blind spots, data exposure risks, and compliance liabilities. Governance provides the guardrails to scale AI with confidence.
AI Data Exposure
Identify and reduce risks from sensitive intellectual property, PII, and financial records being surfaced through AI applications and agents.
AI Access & Identity
Govern who can access AI applications, agents, data repositories, and tools with role-based boundaries and conditional access policies.
AI Risk & Compliance
Identify organizational AI risks and align governance controls with emerging regulatory frameworks including ISO/IEC 42001 and EU AI Act.
AI Usage Visibility
Monitor enterprise AI interactions, shadow AI tools, custom agent execution, and emerging security vulnerabilities across the cloud.
Responsible AI
Establish enforceable policies and ethical controls for trustworthy, transparent, and accountable enterprise AI adoption.
What AI Governance Problems Can We Solve?
Translating complex enterprise security concerns into structured, enforceable Microsoft governance controls.
AI Usage & Data Risk Assessment
Discover unmonitored shadow AI tools, audit sensitive data ingestion, and implement Microsoft Defender cloud app guardrails.
Data Access & Governance Review
Conduct SharePoint permission scans, remediate overshared document libraries, and apply Purview sensitivity labels.
AI Agent Governance & Tool Scopes
Engineer runtime authentication boundaries, tool-level permission scopes, and human-in-the-loop approval workflows.
AI Security Posture & Real-Time Monitoring
Deploy Microsoft Purview AI Hub telemetry to track active AI sessions, anomalous prompts, and data loss prevention alerts.
Responsible AI Governance Framework
Formulate practical, role-based AI policies governing prompt hygiene, intellectual property, and content validation.
AI Audit Trails & Compliance Controls
Implement immutable prompt logging, system response archives, and compliance evidence mapping for ISO/IEC 42001.
Our Enterprise AI Governance Framework
A structured, multi-layer control architecture aligning organizational stakeholders, enforceable security policies, and Microsoft compliance technologies.
People
Cross-functional oversight spanning Legal, Risk, CISO, and Business Unit Leaders.
Policy
Responsible AI frameworks, prompt ethics, copyright protection, and data handling rules.
Technology
Microsoft Purview, Entra ID, Defender for Cloud Apps, and Azure AI Content Safety.
AI Governance Maturity Model
Benchmark your organization's current AI governance posture and plan your path to enterprise AI maturity.
Controlled AI Posture
Active Microsoft Purview DLP sensitivity labels, Entra ID Conditional Access, and zero-trust permissions are enforced.
Microsoft Technologies for Enterprise AI Governance
We architect and implement coordinated controls across Microsoft security, identity, compliance, and application platforms.
Microsoft Purview
Data Security, DLP & ComplianceDiscovers sensitive enterprise data, applies automated sensitivity labels, enforces DLP policies around AI prompts, and provides compliance auditing.
Microsoft Entra ID
Identity & Access GovernanceEnforces zero-trust authentication, Conditional Access, Privileged Identity Management (PIM), and role-based authorization for AI tools.
Microsoft Defender
Security Visibility & Threat DefenseMonitors shadow AI usage via Defender for Cloud Apps, detects prompt injection vulnerabilities, and protects cloud AI infrastructure.
Microsoft AI Foundry
Model Evaluation & Safety FiltersProvides model observability, automated safety guardrails, content filtering, and prompt evaluation for custom enterprise AI applications.
Microsoft 365 Copilot
Enterprise Copilot GovernanceConfigures tenant data isolation, restricted SharePoint site access, and administrative controls governing Copilot in Word, Teams, and Excel.
Microsoft Copilot Studio
Autonomous Agent GovernanceGoverns custom AI agents, manages tool authorization scopes, restricts external API connectors, and enforces human oversight controls.
Microsoft Power Platform
Low-Code AI App SecurityEnforces environment-level DLP policies, Dataverse security roles, and ALM pipelines for AI-enabled business applications.
AI Data Governance & Protection
AI systems should only access data they are strictly authorized to process. We configure Microsoft Purview to enforce data boundaries across all enterprise interactions.
Autonomous AI Agent Governance
Autonomous agents execute workflows, call APIs, and make decisions. We engineer strict identity, tool authorization scopes, and human-in-the-loop safeguards.
Responsible AI Governance
Translating ethical principles into measurable, verifiable organizational guardrails.
Fairness
AI systems are engineered and tested to treat all stakeholder cohorts equitably without systemic algorithmic bias.
Reliability & Safety
Rigorous system prompt evaluations and grounding guardrails ensure consistent, predictable enterprise operation.
Privacy & Security
Strict data boundaries respect enterprise intellectual property and personal privacy commitments across all models.
Inclusiveness
AI capabilities are designed to empower diverse workforce groups, supporting varied skill levels and accessibility standards.
Transparency
AI interactions provide clear grounding citations and explainable reasoning to help knowledge workers validate responses.
Accountability
Clearly defined human ownership, incident escalation runbooks, and audit logging for all automated AI agent actions.
Before vs. After AI Governance
How structured Microsoft Purview and Entra governance transforms enterprise AI operations.
Our Enterprise AI Governance Delivery Process
A structured, end-to-end framework to discover shadow AI, evaluate security & compliance risks, enforce Purview DLP boundaries, and govern autonomous AI agents.
AI Discovery & Risk Assessment
Discover active models, shadow AI tools, API endpoints, and sensitive data exposure risks.
Classification & Access Boundaries
Classify data tiers and configure Entra ID role-based access controls for AI applications.
Purview DLP & Policy Guardrails
Enforce automated sensitivity labels, DLP boundaries, and isolate confidential records from AI index.
AI Agent Governance & Controls
Establish agent tool permissions, runtime policy checks, and human-in-the-loop approvals.
Continuous Monitoring & Auditability
Track prompt telemetry, audit access events, and maintain compliance evidence for ISO 42001.
Enterprise AI Risk Management & Compliance
Purview AI Hub & DSPM for AI
01Real-time visibility into all enterprise AI applications, active prompts, and sensitive data exposure alerts.
Sensitivity Labels & DLP Guardrails
02Entra ID Zero-Trust AI Access Boundaries
03Autonomous AI Agent Tool Permissions
04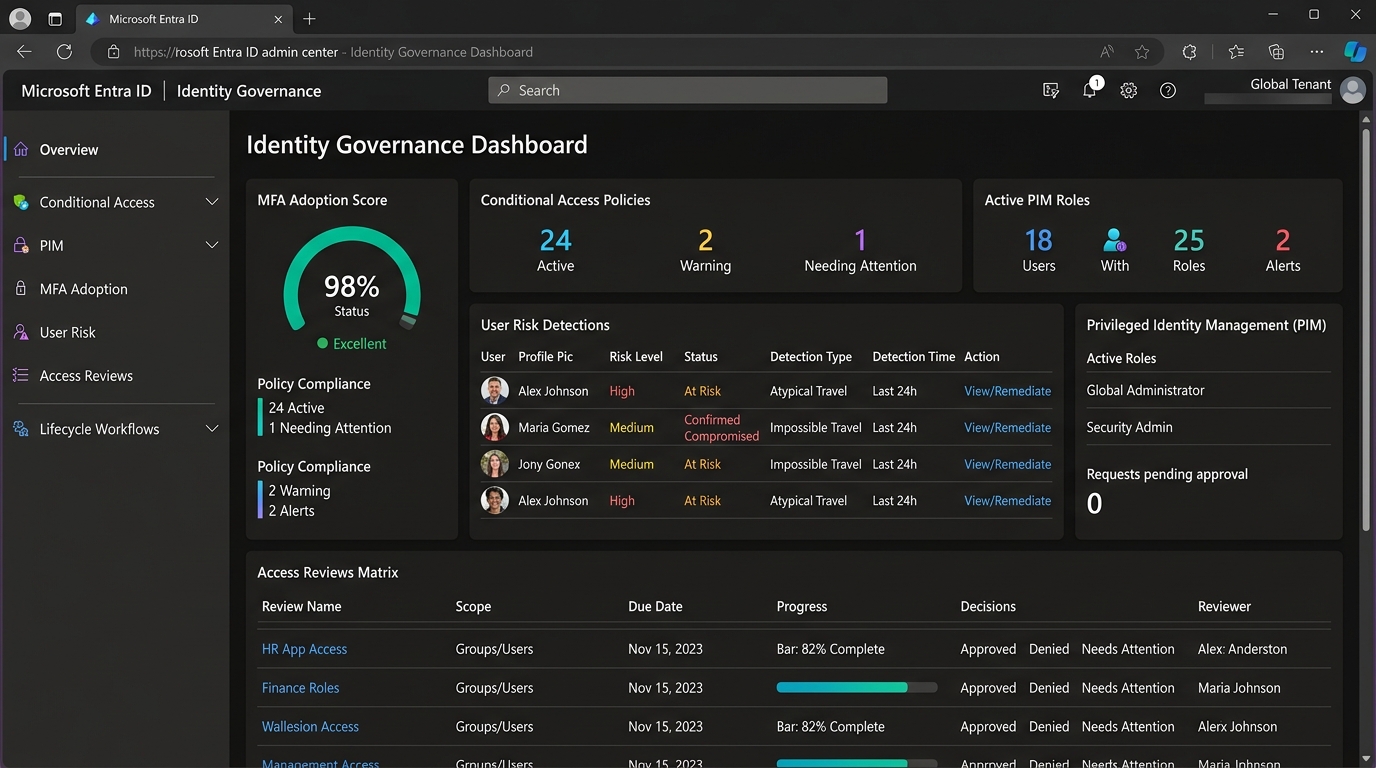
Enterprise AI Governance & Risk Assessment
Evaluate your enterprise AI data boundaries, agent permissions, Purview DLP controls, and compliance maturity.
Got Questions? We Have Answers.
Everything you need to know about our Microsoft 365, Copilot & AI implementation services.
What is enterprise AI governance?
Enterprise AI governance is the comprehensive framework of people, policies, and technical controls used to ensure an organization's AI systems—including Microsoft 365 Copilot, custom AI agents, and LLMs—operate securely, ethically, transparently, and in compliance with legal and organizational standards.
Why does an enterprise need AI governance before scaling Copilot or AI agents?
Without governance, AI tools can surface overshared confidential files, expose sensitive customer PII, call unauthorized external APIs, or generate unvetted responses. Governance establishes identity boundaries, Purview DLP controls, and human oversight so organizations can scale AI safely.
How do you assess enterprise AI risk and shadow AI usage?
We perform an AI Governance & Risk Assessment using discovery scans, Microsoft Defender for Cloud Apps telemetry, SharePoint permission audits, and identity reviews to map active AI tools, identify overshared repositories, and calculate your AI Governance Readiness score.
How does Microsoft Purview support AI governance?
Microsoft Purview provides automated data classification, sensitivity labels, Data Loss Prevention (DLP) policies, and audit logging. Copilot and supported AI tools respect Purview sensitivity labels in real time, preventing restricted data from being referenced by unauthorized users.
How do you govern autonomous AI agents and prevent unauthorized API actions?
We implement an agent governance architecture covering agent identity (Entra Service Principals), granular tool/API authorization scopes, runtime policy validation, human-in-the-loop approvals for sensitive workflows, and immutable audit logs.
How do you solve the risk of SharePoint over-sharing before deploying Microsoft 365 Copilot?
We conduct a Copilot Data Readiness scan to identify overly broad permissions (e.g., 'Everyone except external users'), remediate exposed document libraries, apply restricted SharePoint access policies, and establish structured metadata taxonomies.
What is the difference between Microsoft Entra ID and Microsoft Purview in AI governance?
Microsoft Entra ID governs identity, authentication, and user/agent access permissions (who can access which AI service). Microsoft Purview governs the data itself—classifying sensitivity, preventing data leakage, and maintaining compliance audit trails.
How do we get started with an AI Governance Assessment?
You can request an AI Governance Assessment with our consulting team. We will analyze your Microsoft 365 tenant, review identity and data security baselines, audit custom agent workflows, and deliver an actionable governance roadmap.